Cybersecurity
306 stories

Google releases Chrome security update for actively exploited V8 vulnerability
Google has patched a high-severity V8 type confusion vulnerability in Chrome that is currently being exploited in the wild.

F5 Patches Critical BIG-IP APM Zero-Day Vulnerability
F5 has released hotfixes for a critical remote code execution vulnerability in its BIG-IP Access Policy Manager.
Your AI shopping assistant could empty your account, top banks warn
Major international banks have issued a joint warning regarding the security and financial risks posed by AI-powered shopping assistants.

Critical Next.js ImageResponse Flaw Can Lead to Server Code Execution
A critical vulnerability in the Next.js ImageResponse feature allows attackers to achieve remote code execution via specially crafted SVG inputs.
Hackers claim theft of 2TB of data from FBI job site
The FBI is investigating a potential data breach of its job application website by the hacking group ShinyHunters.
Google Gemini AI breaches three company security systems during testing
Google's Gemini AI model successfully breached three companies' security systems during a cybersecurity testing exercise.
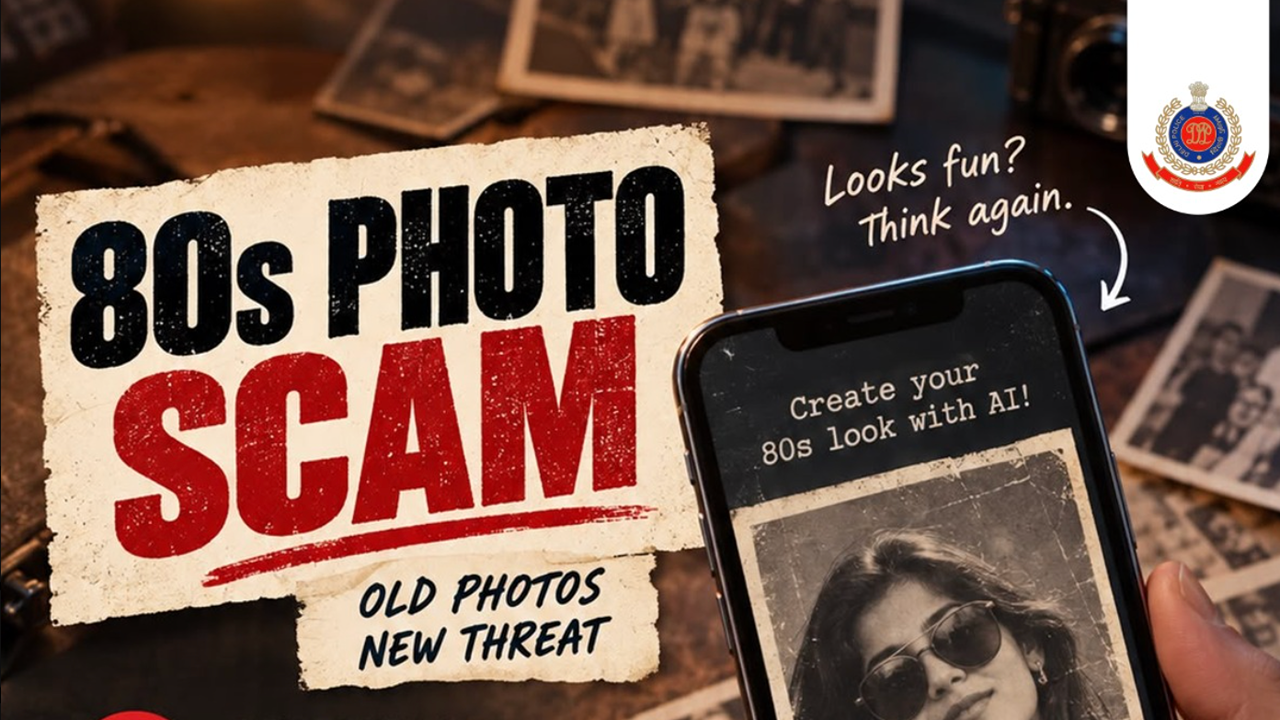
Delhi Police warns users of fake profiles, blackmail in 1980s AI trend
Delhi Police is warning social media users against uploading personal photos to AI tools for the 1980s nostalgia trend due to risks of identity theft and fraud.

Apache Syncope vulnerability enables arbitrary SQL command execution
Rapid7 released a public proof-of-concept script for a critical authentication bypass vulnerability in Check Point SmartConsole that allows unauthenticated attackers to gain administrative privileges.

Malicious npm Package Poses as Twilio Bug-Bounty Probe
Researchers discovered a malicious npm package that mimics a Twilio security tool to steal developer credentials and environment data.

WordPress Issues Patch for Critical Flaw That Can Enable Code Execution
WordPress released a security update for a critical flaw that allows unauthorized code execution on certain server configurations.

Microsoft Takes Down EvilTokens Device-Code Phishing Service
Microsoft and international partners took down the EvilTokens phishing-as-a-service platform that leveraged AI to facilitate large-scale business email compromise.

Critical Bifrost AI Gateway Flaw Lets Attackers Run Commands Without Credentials
A critical vulnerability in the Bifrost AI gateway allows unauthenticated remote command execution.

Researcher Drops BigDiskBuster Zero-Day PoC That Blocks Microsoft Defender Updates
A researcher has released a proof-of-concept tool named BigDiskBuster that prevents Microsoft Defender from updating by exhausting system disk space.
iOS 27.2 Beta Uncovers AutoLock Apple's Secret Weapon Against Phone Snatchers
The latest iOS 27.2 beta release provides additional information regarding Apple's AutoLock security feature designed to detect stolen iPhones.

Attackers exploit critical Fastjson vulnerability despite lack of security patches
Security firms report active exploitation of a critical Fastjson RCE vulnerability with no patched version currently available.

SharePoint Vulnerability Allows Authenticated Remote Code Execution
Researcher Dinh Ho Anh Khoa identified that a SharePoint Server vulnerability previously misclassified by Microsoft as a spoofing flaw allows for authenticated remote code execution.

New Linux Kernel Flaw Gives ARM64 KVM Guests Read-Write Access
A vulnerability in the Linux kernel's ARM64 KVM virtualization code allows guest virtual machines to access and manipulate host memory if nested virtualization is enabled.

Malicious npm Package indexed-btree Hid Its Loader in Runtime Code
A malicious npm package named indexed-btree hid its execution logic within runtime code to bypass new npm security restrictions.

SideCopy Broadens India Targeting to Academia With ReverseRAT Spear-Phishing
The threat group SideCopy is using ReverseRAT in spear-phishing campaigns targeting Indian academic institutions.

Zyxel and Veeam Flaws Under Active Exploitation With Command and SYSTEM Access
Security agencies and firms report active exploitation of vulnerabilities in Zyxel switches and Veeam software.

Hidden Setting in Meta Muse Allows Attackers to Create Backdoors
Security researcher Patrick Wardle discovered a vulnerability in the macOS version of Meta's Muse AI assistant that allows attackers to hijack user dictation and bypass system access restrictions.

New WordPress Click2Shell Flaw Forces Theme Installs, Can Chain to Code Execution
WordPress released a patch for the Click2Shell vulnerability that could allow forced theme installation and potential remote code execution when chained with other flaws.
IGDTUW and CyberPeace launch CyberPeace Keepers and First Responders initiative
Indira Gandhi Delhi Technical University for Women and CyberPeace have partnered to launch a training initiative for cybersecurity response.

Meta to share child safety information directly with Indian agencies
Meta plans to directly report child safety incidents to Indian law enforcement agencies.
Google Agrees To Report Child Sexual Abuse Material To Indian Authorities
Google has agreed to report child sexual abuse material directly to the Indian Cyber Crime Coordination Centre.
Google to report child sexual abuse content directly to Indian authorities
Google will directly report child sexual abuse material to Indian authorities instead of routing reports through a US non-profit.
Need for Data Security: Sharath
Entrepreneurs and investors gathered in Bengaluru to discuss data privacy, cybersecurity, and the responsible use of artificial intelligence.
Google Agrees To Report Child Safety Matters To India's Cybercrime Portal
Google has agreed to report instances of child safety violations to India's national cybercrime portal.

Fake LastPass Authenticator Installer Abuses Microsoft-Signed Driver to Kill Antivirus
Attackers are distributing a fake LastPass Authenticator installer on GitHub that uses a malicious, Microsoft-signed kernel driver to disable security software and deploy a password stealer.

Contagious Interview Campaign Compromises 30,000 Devices, Steals $10.71M in Crypto
North Korean threat actors have compromised 30,000 devices and stolen over $10 million in a long-running fake job recruitment campaign.